Atlas AIDR: AI Detection and Response

Secure AI Activity Across Your Organization

AI coding tools and agentic AI act with real credentials and broad permissions. Atlas AIDR turns every AI session into an attributable record, with detection & response built in.

Build a Quote
Build a Quote

Jump To

AI Estate Visibility, Governance and Control

Know Your AI Estate

Users, teams, and workstations tied to every AI session.

Agent Supply Chain Governance

Live inventory of the MCP servers agents use.

Detect and Respond

Screen for secrets and prompt injection before the model sees it.

Account for Spend

Session timeline and token economics per request.

Detection and Response for AI

Atlas AIDR closes the gap left by AI tools your existing security stack was never built to see. It plugs directly into the Atlas Platform for AI governance, detection and response, without blocking adoption.
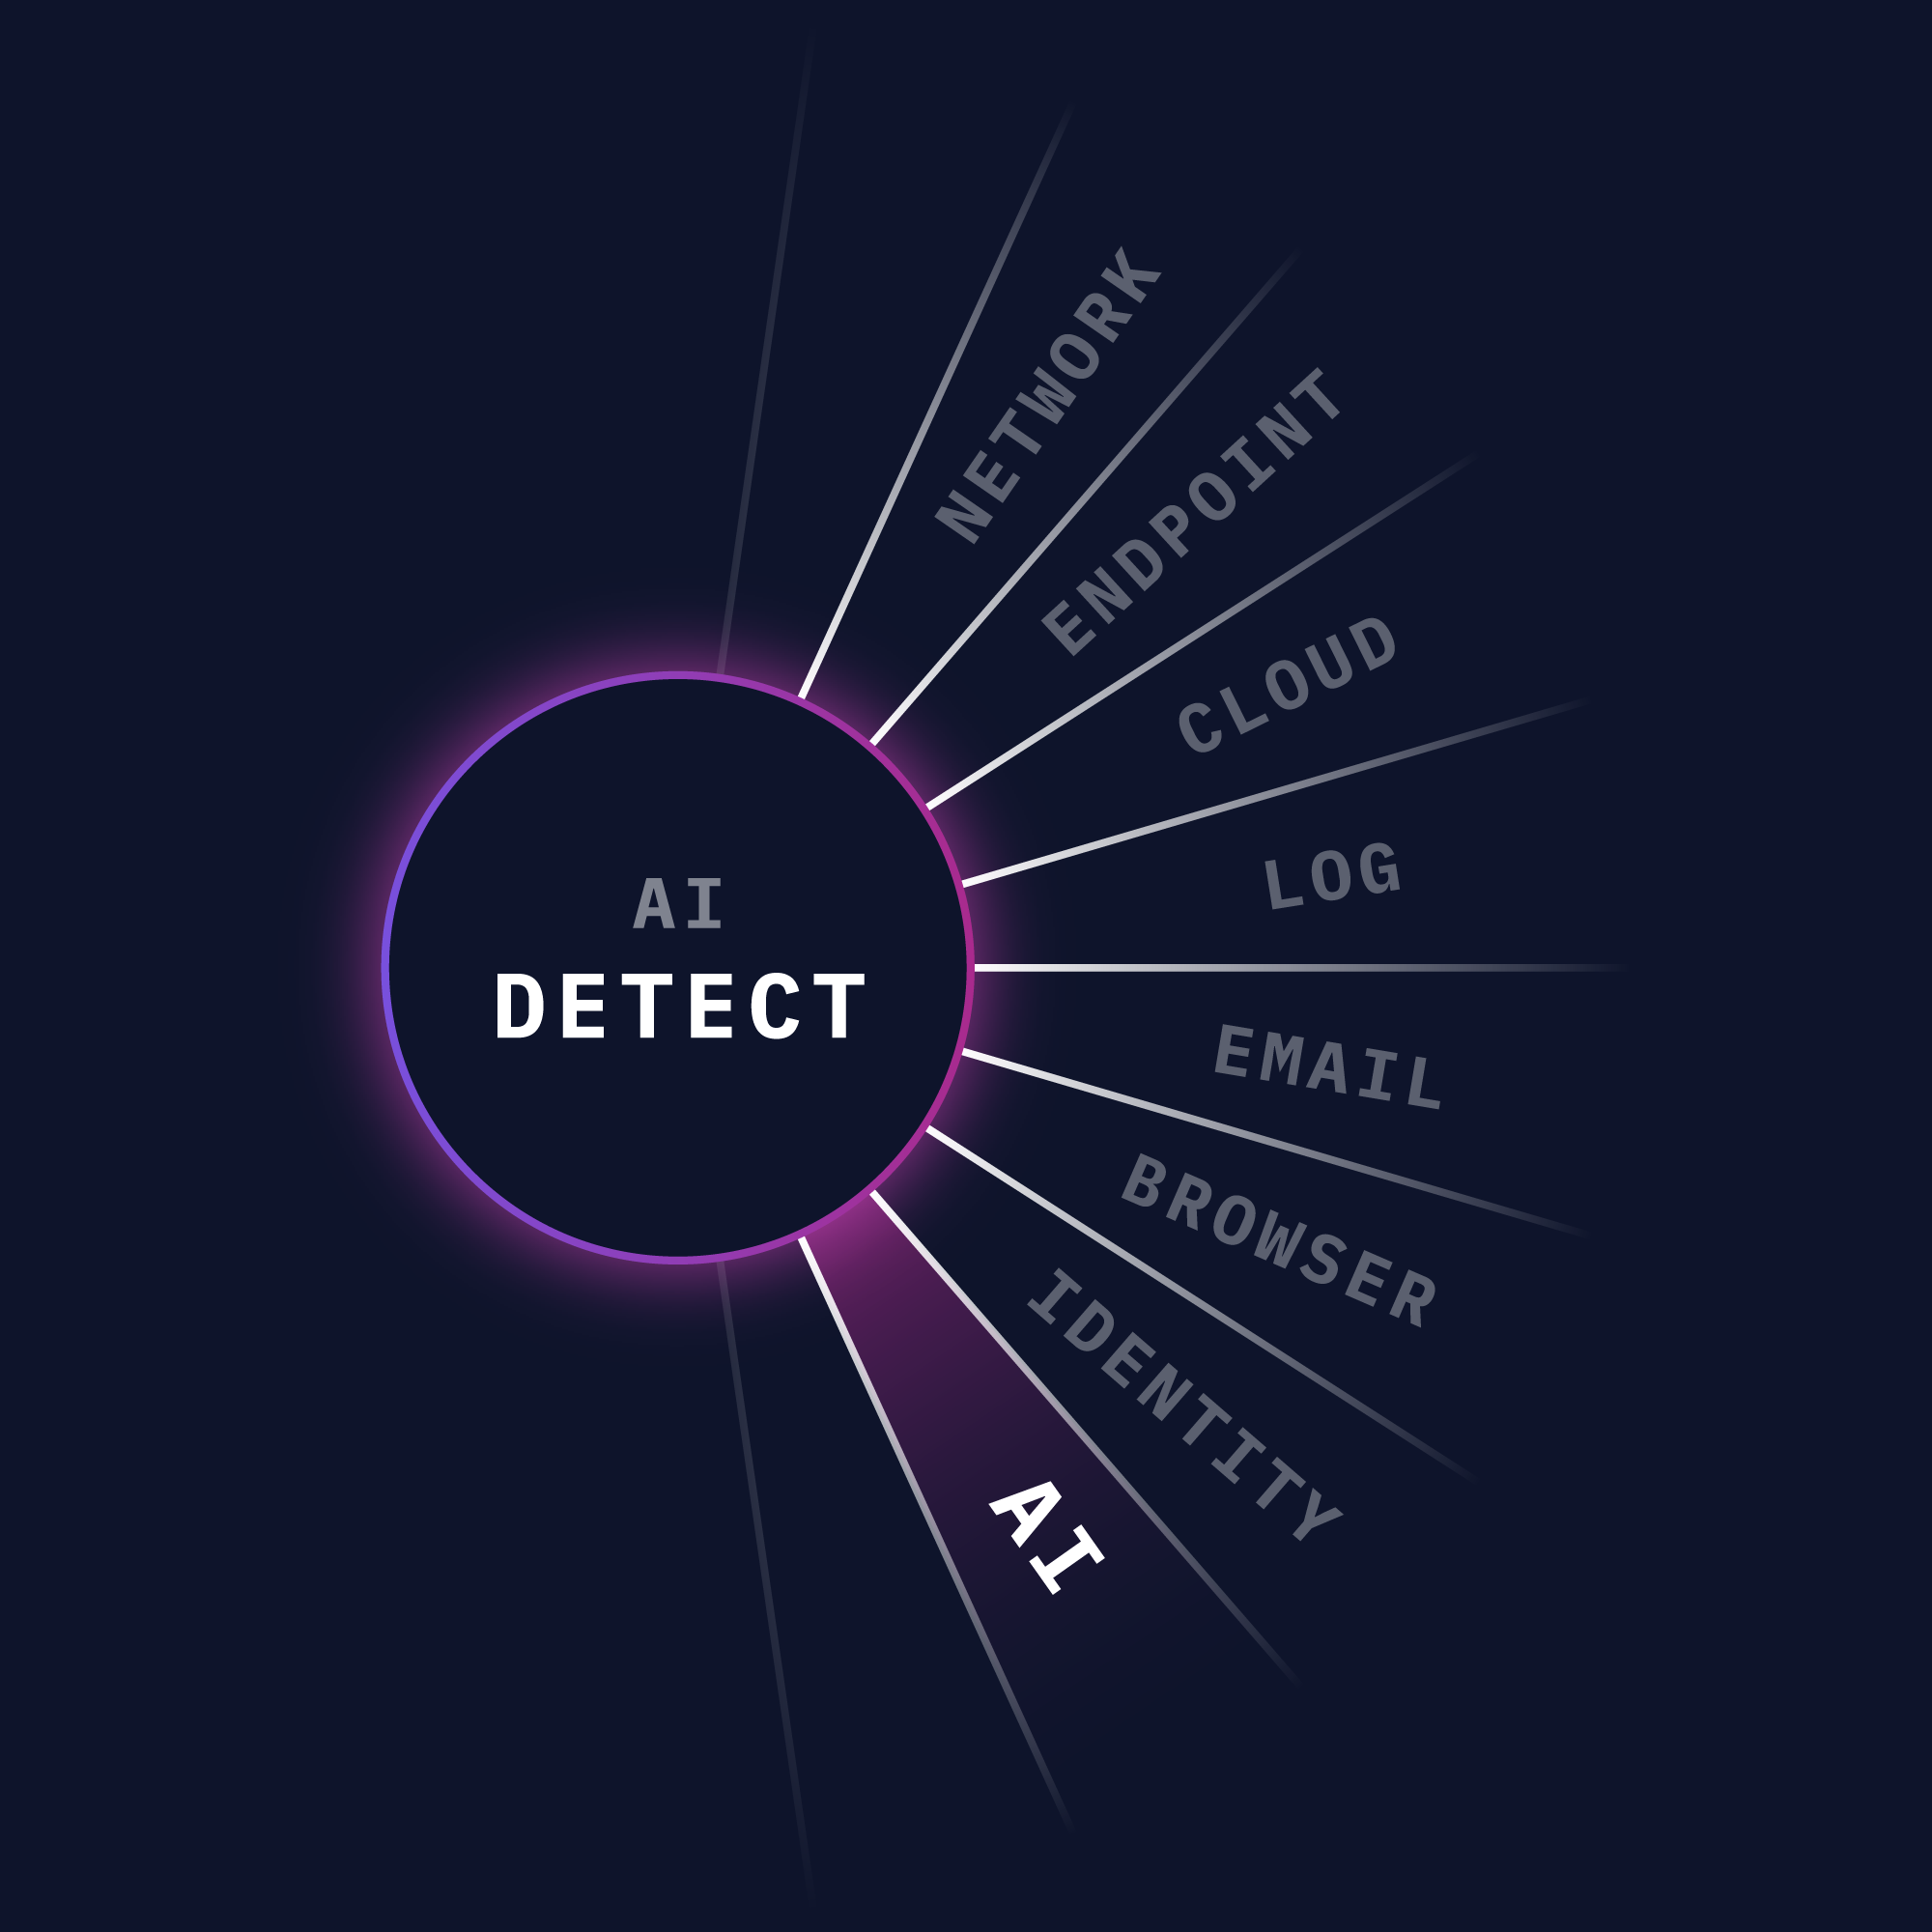
AI Detect signal diagram covering network, endpoint, cloud, log, email, browser, identity, and AI signals

We detect and respond to the following AI risks:

  • MCP servers pulled into agent workflows
  • Prompt-injection attempts targeting models and agents
  • Secrets exposure in prompts and responses
  • AI spend surfaced from day one

How We Help:

  • Inline proxy, or network-level visibility
  • Correlation with endpoint and network telemetry in the same Atlas console as the rest of your estate
  • 24/7 SOC and TRU investigation of AI security incidents

Your Outcomes:

  • An auditable record of AI activity
  • Secrets caught before it causes harm
  • Prompt-injection attempts screened and blocked
  • Innovate at the speed of AI adoption
  • Anomalous AI spend surfaced from day one

On the Horizon

We're continuing to build out Atlas AIDR. Coming soon:

New Deployment Options

Connect Atlas through an LLM Gateway, or bring your own third-party LLM Gateway.

Expanded Detection and Response

New coverage from our Threat Response Unit (TRU), built on the same threat research and content development behind our MDR services.
See Atlas AIDR in Action

Get real-time observability across every desktop AI agent interaction: security findings, active sessions, token spend, supply-chain status, and a full feed of events, in one view. Atlas AIDR covers multiple model providers inline and gets you to your first captured session in minutes.

Typical AI Security Tooling vs Atlas AIDR

CAPABILITY
TYPICAL AI
SECURITY TOOLING
ATLAS AIDR
Inventory of AI agents, models, and providers
Prompt, response, and tool-call capture
Secrets and prompt-injection screening for routed traffic
MCP server and tool inventory attributed to teams
Monitoring for server behavior change after approval
Token economics per request and anomalous-spend alerting
Full-session capture in Atlas
Correlation with endpoint and network telemetry as the rest of your estate
24/7 human-verified investigation included, no extra modules

AI Security FAQ

What is Atlas AIDR?

Atlas AIDR (AI Detection and Response) is an AI security service that gives you observability, threat detection, and control across every agent, model, and MCP server in your environment. It turns every AI session into an attributable record, tied to a user, team, and workstation, with secrets and prompt-injection screening enforced inline for routed traffic. When a detection fires on AI telemetry, eSentire's SOC investigates and responds.

How does Atlas AIDR work?

Atlas AIDR works in five steps.

  1. First, we connect: the agent installs once per workstation, by policy or a single command, and routes traffic through an inline proxy wherever you want redaction and cost tracking per request.
  2. Next, we capture: every prompt, response, tool call, and token becomes an attributable record, tied to a user, team, and workstation.
  3. Then we inspect: Secrets and prompt injection is screened in the request path, before content reaches the model.
  4. From there, we enforce: block rules, budgets, and your own business-logic rules are applied in-flight, on an SSO-governed control plane.
  5. Finally, we respond: high-severity findings are surfaced to the same Atlas console your SOC works from, and TRU hunts proactively, before the attacker moves.
What AI risks does Atlas AIDR address?

Atlas AIDR is built for the risks that come with rapid AI adoption: third-party MCP servers pulled into agent workflows without review, prompt-injection attacks, PII exposure in prompts and responses, and anomalous token spend that can signal compromise.

How is Atlas AIDR different from typical AI security tooling?

Most AI security tooling stops at inventory and prompt capture. Atlas AIDR adds MCP server and tool inventory attributed to teams, monitoring for server behavior change after approval, token economics per request with spend anomalies surfaced in costs, full-session capture in Atlas, correlation with your endpoint and network telemetry in the same Atlas console as the rest of your estate, and 24/7 human-verified investigation included, with no extra modules.

How quickly can I get visibility into my organization's AI usage with Atlas AIDR?

Atlas AIDR is designed to get you to your first captured session in minutes, covering multiple model providers inline, and capturing 100% of every AI session from prompt to tool call.

Security Leaders Count on eSentire to Prevent Business Disruption

G2 logo with 4.7 out of 5 star rating for eSentire eSentire G2 Fall 2026 badges: Leader, Mid-Market Leader, Enterprise Leader, Users Love Us, and System Security Leader

AI Security Resources

Ready to See What Your AI Is Doing?

Assume your agents are already doing things you cannot account for.