eSentire is a leader in Controlled Autonomy SecOps, protecting thousands of organizations across 35+ industries around the world. Founded in 2001, the company’s Controlled Autonomy SecOps operating model pairs agentic AI operatives with engineered human-judgment controls, delivering expert-depth security outcomes at machine speed without ceding accountability to opaque automation.
We provide sophisticated cybersecurity solutions for Managed Security Service Providers (MSSPs), Managed Service Providers (MSPs), and Value-Added Resellers (VARs). Find out why you should partner with eSentire, the Authority in Managed Detection and Response, today.
The Managed Detection and Response (MDR) market is growing rapidly, with some reports projecting growth of up to 9.5 billion by 2028. In this saturated market, choosing the right provider to secure your organization can be challenging. We believe that analyst research and reports, like the Gartner® Market Guide for Managed Detection and Response, play a crucial role in helping you evaluate security vendors.
To us, these reports provide a comprehensive evaluation of the MDR market, key trends, and emerging technologies, allowing you to assess security vendors and choose the one which best aligns with your organization’s needs.
What is Gartner?
Gartner delivers actionable, objective insights to executives and their teams. Its expert guidance and tools enable faster, smarter decisions and stronger performance on an organization’s mission-critical priorities.
The Market Guide for Managed Detection and Response by Gartner
“Gartner defines managed detection and response (MDR) services as those that provide customers with remotely delivered security operations center (SOC) functions. These functions allow organizations to perform rapid detection, analysis, investigation and response through threat disruption and containment.”
In our experience, the Market Guide for Managed Detection and Response is one of the most popular assets in the extensive portfolio of cybersecurity research from Gartner. We feel this report provides a comprehensive overview of the Managed Detection and Response market landscape, highlighting key trends, challenges, and opportunities for organizations seeking MDR solutions.
The latest edition of the Gartner Market Guide for Managed Detection and Response states, “MDR services provide customers with remotely delivered, AI-augmented, human-led, turnkey, modern SOC functions, ultimately delivering cyberattack disruption and containment.”
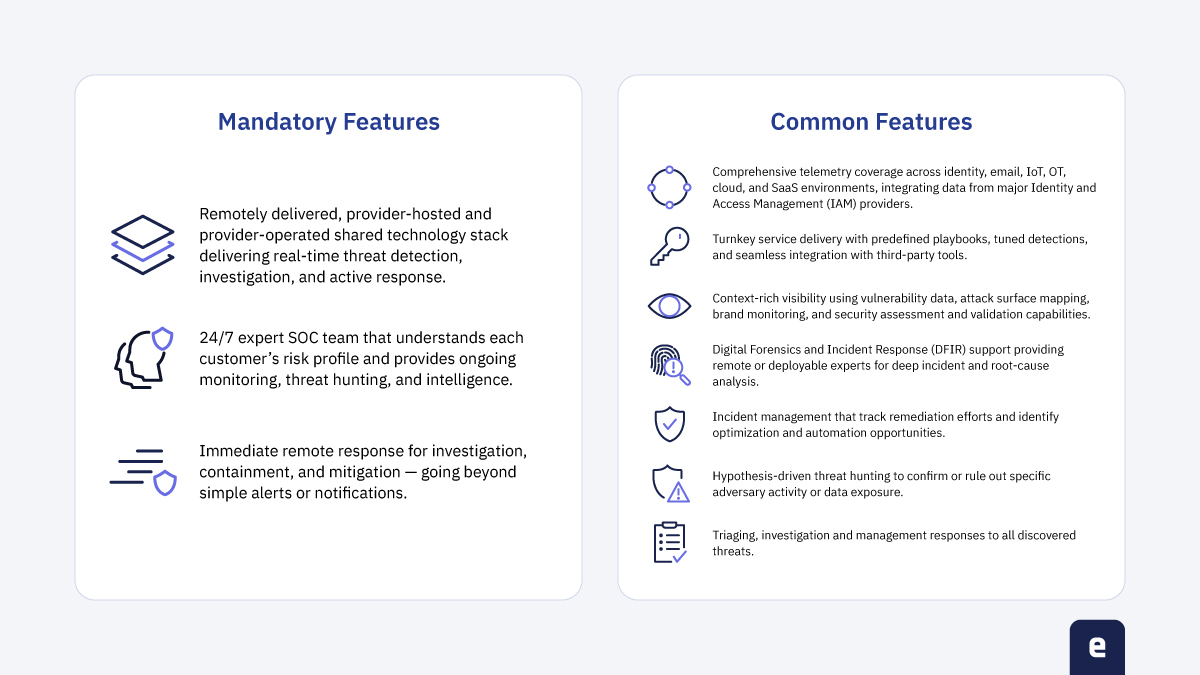
Here is how we interpret the Gartner® Market Guide’s view of what a Managed Detection and Response provider should have:
The report states, “Gartner estimates that more than 600 providers in this market claim to offer MDR services.” However, security leaders regularly face challenges distinguishing between real MDR and fake MDR services which overpromise and underdeliver on security outcomes.
We believe that the 2026 report sharpens that warning. Gartner notes that a growing number of providers market their offerings as MDR without delivering the human-led investigation and response the research defines as core to the category, and flags that confusion around AI-driven or autonomous MDR claims is adding to the problem. eSentire is named as a Representative Vendor in the 2026 Market Guide, evaluated against that same outcome-driven definition.
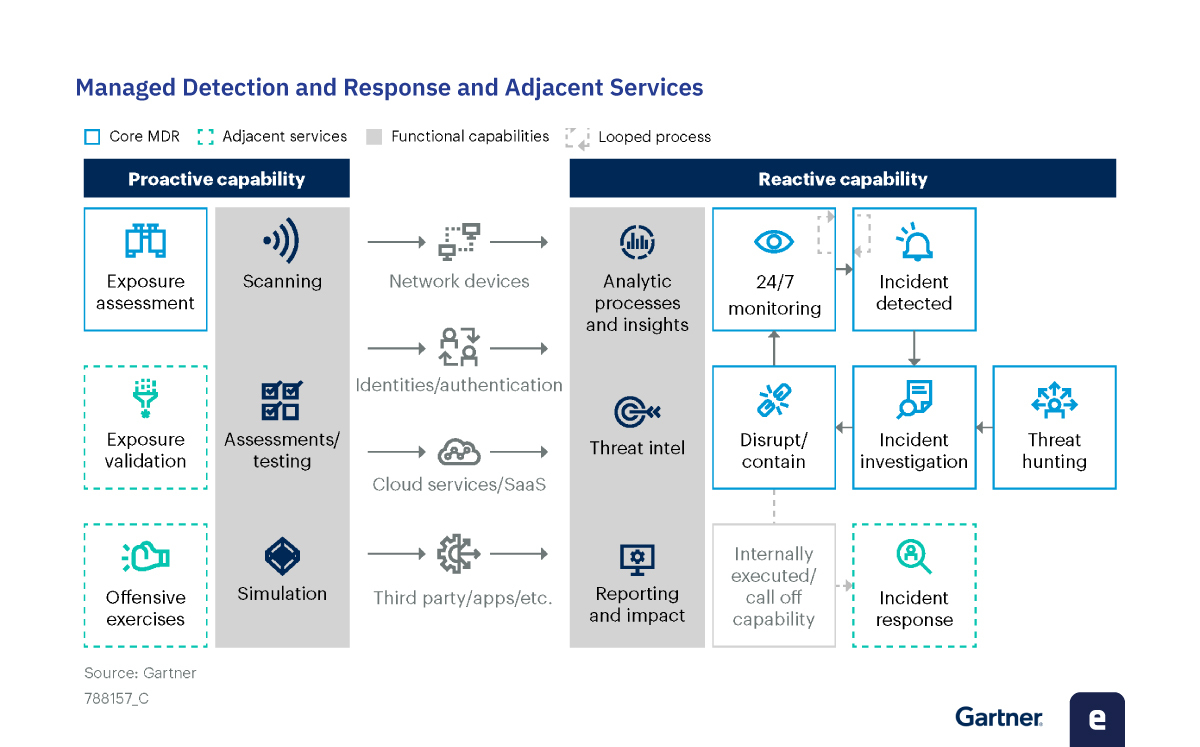
In the latest report, Gartner defines core MDR services and adjacent services as follows:
In this highly saturated market, we believe organizations often turn to Gartner for insights and guidance when evaluating different MDR providers.
MDR Gartner FAQ
Q. What are the core capabilities Gartner says an MDR provider should have?
According to the 2026 Market Guide, it’s our view that an MDR provider should deliver on five mandatory capabilities: a remotely delivered, coordinated technology stack for real-time detection and response; 24/7 staffing with threat monitoring and response expertise; immediate remote mitigative response and containment, pre-approved by the customer; telemetry coverage across identity, email/collaboration, IoT/OT, and cloud/SaaS; and turnkey delivery built on predefined, pretuned processes.
Q. What are the other common features Gartner says an MDR provider can have?
We believe the Gartner 2026 report lists optional features that extend beyond the mandatory baseline: additional contextual data on security exposures, including breach and attack simulation (BAS) capabilities; digital forensics and incident response (DFIR) retainer services with call-off staff; incident management capabilities that track and suggest remediation and automation improvements; hypothesis-driven threat hunting targeted at specific users or exposed data; and unrestricted triage, investigation, and management of all discovered threats, with incident tickets that map attacker objectives and business impact.
Q. How often is the Market Guide for Managed Detection and Response updated?
In our experience, the Market Guide is typically updated annually, with a new version released once a year to reflect the latest developments and trends in the rapidly evolving MDR market.
Q. How can you access the MDR Gartner Market Guide?
It’s important to note that we believe that the Gartner selection process aims to be objective and based on comprehensive data collection and analysis.
The specific process details might vary from year to year. Still, we feel the Gartner commitment to thorough research and analysis ensures that their reports provide valuable insights for organizations evaluating MDR service providers.
Q. Does Gartner provide additional information in their Managed Detection and Response Services Reviews and Ratings data?
1. Gartner, Market Guide for Managed Detection and Response, 9 September 2026, By Andrew Davies, Angel Berrios, Eric Ahlm, Darren Livingstone, Craig Lawson
2. Gartner does not endorse any company, vendor, product or service depicted in its publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner publications consist of the opinions of Gartner’s business and technology insights organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this publication, including any warranties of merchantability or fitness for a particular purpose.
3. GARTNER is a trademark of Gartner, Inc. and/or its affiliates.
This graphic was published by Gartner, Inc. as part of a larger research document and should be evaluated in the context of the entire document. The Gartner document is available upon request from eSentire.
eSentire Managed Detection and Response
Our MDR service combines cutting-edge Extended Detection and Response (XDR) technology, multi-signal threat intelligence and 24/7 Elite Threat Hunters to help you build a world-class security operation today. Our threat protection is unparalleled in the industry - we see and stop cyberattacks other cybersecurity providers and technologies miss, delivering the most complete response and protection.