Connects to any signal across any vendor stack and powers adaptive AI Operatives that expose, detect, and neutralize cyberattacks.
Atlas Operations CenterSee what our SOC sees, review investigations, and see how we are protecting your business.
Technology IntegrationsAtlas connects to any signal across your current security tools. Whatever you're running, we're running with you.
Extend your team with immediate expertise, hands-on remediation, and the human accountability layer that boards, regulators, and cyber insurers require.
Threat Response UnitProactive threat intelligence, original threat research and a world-class team of seasoned industry veterans.
Response and RemediationPairs machine-speed containment with human judgment, delivering full threat response that's policy-bounded, reversible, and explainable.
MDR that moves first, multi-signal attack surface coverage, and 24/7 Elite threat hunters working as one continuous security program across any vendor stack.
Get unlimited Incident Response with threat suppression guarantee- anytime, anywhere.
Atlas Preempt deploys AI Operatives to continuously validate attack paths exposing attacker targets of opportunity before they take advantage.
Protect insurance operations from cyber attacks.
ConstructionSecure project data and jobsite operations.
FinanceDefend financial services from cyber disruption.
LegalSafeguard client data and legal operations.
ManufacturingStop threats before they disrupt production.
Private EquityProtect portfolio companies from cyber risk.
HealthcareDefend patient data and clinical operations.
RetailProtect customer data and retail operations.
Food SupplySecure the food supply chain from cyber threats.
Government and EducationProtect public sector and education systems.
Automotive DealershipsSecure dealership operations and customer data.
Stop ransomware before it spreads.
Identity ResponseStop identity-based cyberattacks.
Zero Day AttacksDetect and respond to zero-day exploits.
Cybersecurity ComplianceMeet regulatory compliance mandates.
Third-Party RiskDefend third-party and supply chain risk.
Cloud MisconfigurationEnd misconfigurations and policy violations.
Cyber RiskAdopt a risk-based security approach.
Mid-Market SecurityMid-market security essentials to prioritize.
Sensitive Data SecurityProtect your most sensitive data.
Cyber InsuranceMeet insurability requirements with MDR.
Cyber Threat IntelligenceOperationalize cyber threat intelligence.
Security LeadershipBuild a proven security program.
eSentire is a leader in Controlled Autonomy SecOps, protecting thousands of organizations across 35+ industries around the world. Founded in 2001, the company’s Controlled Autonomy SecOps operating model pairs agentic AI operatives with engineered human-judgment controls, delivering expert-depth security outcomes at machine speed without ceding accountability to opaque automation.
About Us Leadership Careers Event Calendar → Newsroom → Aston Villa Football Club →
We provide sophisticated cybersecurity solutions for Managed Security Service Providers (MSSPs), Managed Service Providers (MSPs), and Value-Added Resellers (VARs). Find out why you should partner with eSentire, the Authority in Managed Detection and Response, today.
Search our site
Multi-Signal MDR with 300+ technology integrations to support your existing investments.
24/7 SOC-as-a-Service with unlimited threat hunting and incident handling.
We offer three flexible MDR pricing packages that can be customized to your unique needs.
The latest security advisories, blogs, reports, industry publications and webinars published by TRU.
Compare eSentire to other Managed Detection and Response vendors to see how we stack up against the competition.
See why thousands of organizations globally have chosen eSentire for our MDR Solution.
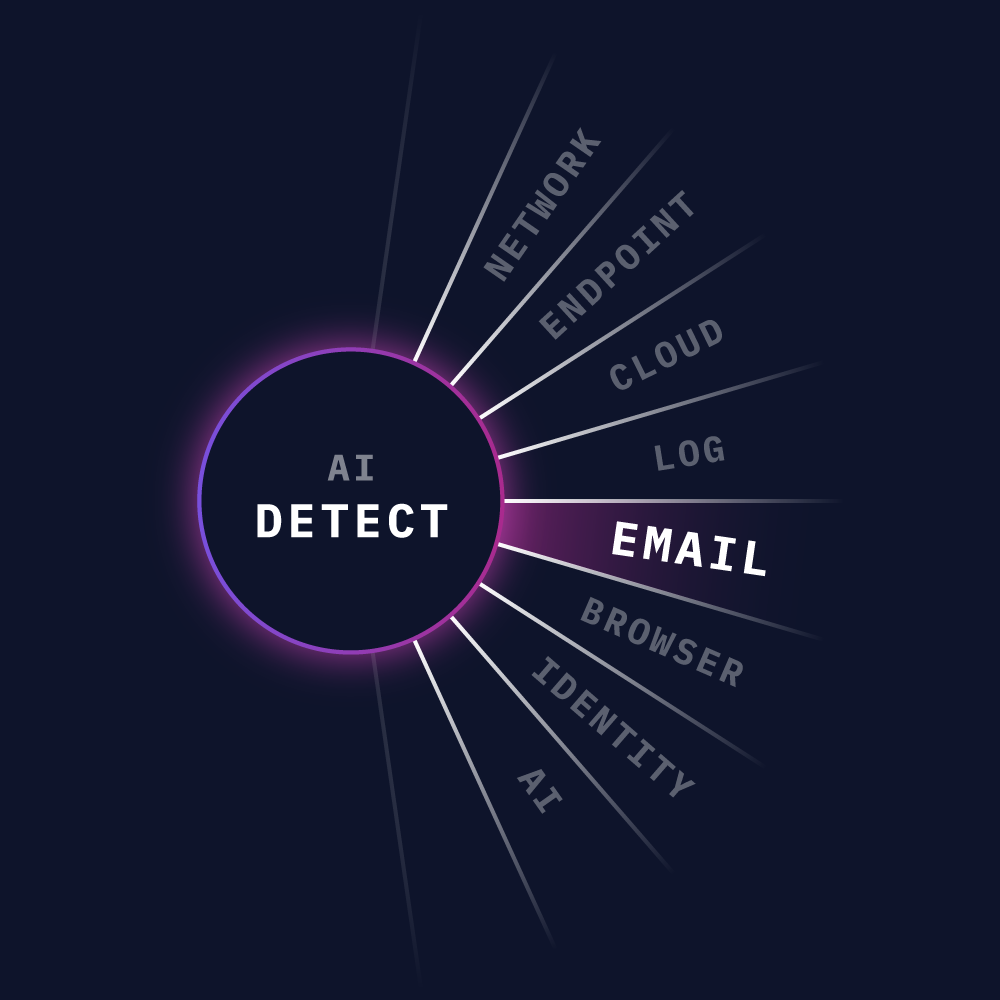
Atlas turns email into a signal our 24/7 SOC can act on. Connect the email security you already run, or go deeper with Atlas Email Security.
Talk to an ExpertHow Email Signal Gets Into Atlas
Atlas Email Security
See It in Action
Comparison
FAQ
Resources
A convincing invoice. A fake IT ticket. A QR code that opens a fake sign-in page. Attackers don't need an exploit when an inbox will do, and AI now writes a fresh lure in minutes.
1,450%
rise in email bombing and IT impersonation
eSentire 2026 Threat Report
14 Minutes
from credential theft to exploitation with Phishing-as-a-Service
eSentire 2026 Threat Report
Proofpoint, Microsoft 365 or the logs from your email gateway. Atlas takes the signal from the tools you already own.
Email alerts land in the same Atlas finding as endpoint, identity, network and cloud activity.
Our SOC acts back through your email tool. With Atlas Email Security, clear threats are remediated automatically and our SOC investigates and removes the rest from every inbox.
Employees report what slipped through. Our SOC investigates every report, closes the false ones and removes the real ones.
Start with the email security you already have. Go deeper when you're ready.
Our deepest coverage. A native detection engine inside Atlas with explainable verdicts, automatic remediation and SOC investigation.
Proofpoint alerts land in Atlas, and our SOC responds back through Proofpoint. Mimecast coming soon.
Your employees' report button, wired to our SOC. Works with the Microsoft 365 and Proofpoint report buttons.
Logs from your email protection tools, ingested through Atlas Log for investigation, hunting and context.
Atlas Email Security · Add-On
with Sublime
Atlas Email Security adds Sublime as a native engine inside Atlas. Clear threats are remediated automatically. Anything else goes to our SOC. It connects to Microsoft 365 over API with no MX changes, and it’s an add-on to any Atlas Package, with User Reported Phishing included.
Reads intent, sender behavior, links, attachments and QR codes. Clear threats are quarantined, moved to spam or bannered.
Each flagged email carries its Attack Score and detection logic.
Our SOC pulls the message or the whole campaign, including calendar invites, from every mailbox.
Email is one more signal in the Atlas loop. Our SOC correlates it with the rest of your environment, so a phishing email, the click and the sign-in that followed are worked as one attack.
We're continuing to expand email coverage in Atlas. Coming soon:
Atlas Email Security and User Reported Phishing for Gmail.
Mimecast alerts in the same Atlas investigation, with response back through Mimecast, plus the Mimecast report button.
A phishing email is rarely the whole story. Here's what happens when one reaches an inbox.
Your email security raises an alert, or an employee reports the message.
The alert lands in Atlas with the rest of your signals, not in a separate console.
Atlas AI and our analysts look across your endpoint, identity, network and cloud activity for what happened next.
Respond sthrough your email tool, within your rules, pulling the message or campaign from every mailbox.
The alert, evidence and every action in one Atlas Finding.
That's the difference between deleting an email and stopping an attack.
Our SOC acts within the response settings you choose. Nothing happens outside them.
Every alert arrives in Atlas with the evidence behind it, so you can check our work.
Allow and block lists, exclusions and quarantine release stay with your team.
Our 24/7 analysts own every response and record every action. They never log in to your mailboxes.
It's how eSentire brings email into Atlas as a signal. Atlas takes in alerts and logs from your email security, plus the phishing your employees report. Our 24/7 SOC investigates each one alongside your endpoint, identity, network and cloud activity, and responds. For the deepest coverage, Atlas Email Security adds a native email detection engine inside Atlas.
Four ways. Atlas Log ingests logs from your email protection tools. User Reported Phishing sends your employees' reports to our SOC. Bi-directional integrations bring Proofpoint alerts into Atlas and send response back through Proofpoint. Atlas Email Security, with Sublime, inspects every message natively inside Atlas.
No. Atlas works with the email security you already run. If you want deeper detection and response, Atlas Email Security runs alongside your gateway or replaces it.
Yes. Atlas connects to Proofpoint in both directions. Proofpoint alerts land in the same Atlas investigation as the rest of your environment, and our SOC responds back through Proofpoint. The Proofpoint report button also works with User Reported Phishing.
A bi-directional Mimecast integration is coming soon. Atlas can ingest Mimecast logs today through Atlas Log.
Atlas Email Security is an add-on to any Atlas Package for organizations that want our deepest email coverage. It uses Sublime as a native engine inside Atlas to check every message as it lands and automatically remediate clear threats, explain each verdict with its Attack Score and detection logic, and send anything that needs further investigation to our SOC analysts, who can remove a message or whole campaign from every inbox. User Reported Phishing is included.
Employees report a suspicious email with the report button they already use. Our SOC investigates every report, closes false reports and removes real phishing. It works with the Microsoft 365 and Proofpoint report buttons today.
It depends on how email reaches Atlas. With Proofpoint, our SOC responds back through Proofpoint. With Atlas Email Security, clear threats are remediated automatically at delivery. Anything that needs further investigation goes to our analysts, who quarantine or trash the message or the whole campaign, and remove calendar invites, from every mailbox. Every action runs within the response settings you choose and is recorded in the Atlas finding.
No. Integrations and Atlas Email Security connect over API, so your mail keeps flowing the way it does today.
Atlas Email Security supports Microsoft 365 today and augments Microsoft Defender for Office 365. Google Workspace support is coming soon.
Your email security already sees the first move. Let our SOC see the rest of the attack.