YOUR TOOLS. CONTROLLED AUTONOMY. MDR EVOLVED.

The Atlas Platform

MDR that moves first. Agentic AI and human experts on your side, 24/7.

Deploy Atlas for 30 Days Free
DEPLOY ATLAS FREE FOR 30 DAYS

Jump To

Controlled Autonomy SecOps

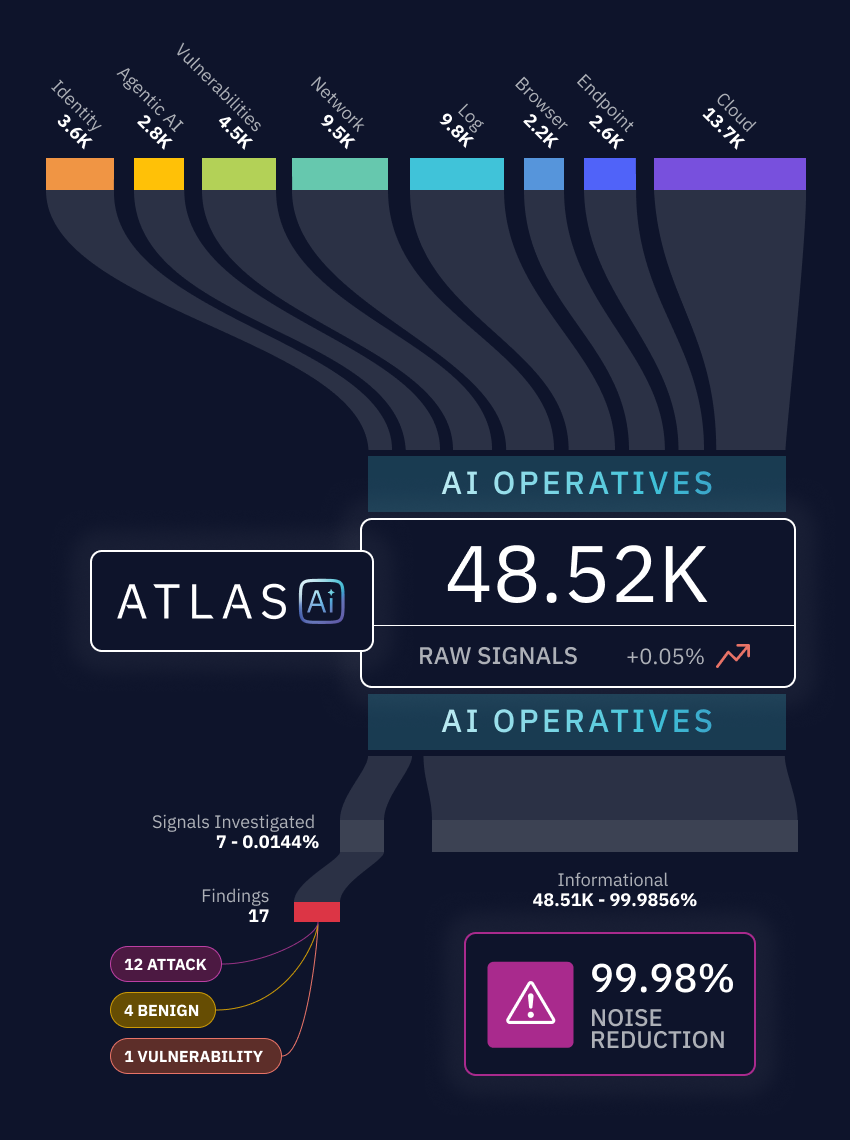
Atlas combines real-world attacker intelligence, elite agentic AI operatives, and human expertise on the loop. MDR has evolved to move first, delivering the speed, context, and precision needed to stay ahead of adversaries.

Network
Endpoint
Cloud
Log
Email
Browser
Identity
AI
Controlled Autonomy SecOps

Human + AI Reasoning

95% tier-3 analyst validation alignment

Response Actions

TCP disruption, host isolation, user suspension

Threat Intel & Hunting

200+ threat protections added daily

Offensive Arsenal

Hundreds of real-world tools and agentic hacking tools

Preempt Autonomous pen testing & CTEM
Detect Managed detection & response
Respond Autonomous response

See Atlas in Action


Every Integration, No Blind Spots

You're managing dozens of tools that were never built to talk to each other. Whatever you're running, we're running with you. Atlas meets your stack where it is.

VIEW INTEGRATIONS

One Continuous Loop. Always Evolving.

Atlas AI operatives find exposures, sharpen detection and respond at machine speed. Patches wait for your approval.

Preempt

Probes your defenses like an attacker would.
  • Autonomous Pen TestingHundreds of real-world tools across the kill chain.
  • Stress-test your stackReal adversary simulations prove what’s exploitable.
  • Recurring and autonomousTesting runs on the cadence you set.
  • Every finding feeds the loopFindings sharpen detection and show what to fix.
Explore Offensive Security & CTEM

Detect

Watches every signal surface for threats.
  • Any stack, every signalHundreds of new detections daily, built from real-world investigations, across the stack you have.
  • Multi-signal coverageEndpoint, network, identity, cloud and AI signals, correlated in real time.
  • AI SecurityTrack users, teams, and workstations tied to their AI sessions, alongside a live inventory of agents, models, providers, MCP servers, and tools ready for audit.
  • Real-time detection30+ investigative steps per threat and 95% alignment with senior analysts. Threats are isolated before they spread.
See How MDR Works

Respond

Shut attackers down and close the way in.
  • Full containment and investigationHost isolation, user suspension and TCP disruption at machine speed.
  • Patch management (add-on)Atlas ranks outdated third-party apps by what to fix first and patches them once you approve, from the same console that found them.
  • Every response delivers adaptationEach action closes with measurable improvements, validated by offensive testing.
  • Real Time AI-SecurityRedact PII before it reaches the model, screen for prompt injections at the proxy, and enforce custom business logic rules inline to prevent policy violations instantly.
  • Controlled Autonomous AIHundreds of elite analysts on the loop 24/7, with six-year average tenure.
Discover Autonomous Response

Everyone detects.
eSentire closes the loop.

PROBLEMS
HOW ESENTIRE SOLVES IT
Proprietary stack, vendor lock-in
Every integration across any vendor technology
Vulnerabilities are found, but forgotten
Aggregate exposures, validate exploitability and patch outdated apps with Atlas Patch Management once you approve
AI that forgets what it learned yesterday
Elite AI built on 25 years of SOC investigations with humans-on-the-loop
Offensive insights are siloed, lost in a pdf
Hundreds of Autonomous Pen Testing tools always evolving with Detection + Response
Understanding AI usage, what data is accessed, and what it costs
Turn AI sessions into live, auditable records, with security and spend controls enforced

AI Security Resources

Run Atlas Free for 30 Days

Connect your stack. See real threats in your environment, not a demo.

Security Operations Platform FAQ

What is the Atlas Security Operations Platform?

Atlas is eSentire's Controlled Autonomy SecOps platform. It connects to your entire security stack, correlates signals across endpoints, network, identity, email, cloud, SaaS, and more. Leveraging AI operatives, Atlas preempts exposures, detects threat actor activity, and disrupts cyberattacks before they land.

How is Atlas different from other MDR or XDR platforms?

Most MDR and XDR platforms wait for something bad to happen, then respond. Atlas starts with offense. It tests your environment the way a real attacker would, feeds those findings into detection, and uses response actions to immediately shut down the attackers all in a single platform. That's a fundamentally different operating model.

Does Atlas AI act on its own or do humans stay involved?

Atlas investigates, correlates, and recommends, but no host gets isolated, no action gets taken, and no response gets executed without a SOC analyst reviewing and approving it first. No exceptions. Patches wait for approval too, from your own team. AI handles the volume and speed. Humans ensure accuracy, context, and judgment.

What does Atlas integrate with?

Atlas supports the integrations that matter to you, across many signal sources. It's included as part of your eSentire service with no additional setup. Review our integrations or contact us if you would like information on a specific integration.

Do I need to buy Atlas separately?

No. Atlas is the platform that powers your eSentire service. It's not an add-on or upsell — it's the engine underneath everything we deliver.

How quickly can I get value from Atlas?

Atlas ingests telemetry from your existing stack through pre-built integrations, which means time-to-value is measured in hours, not days. Your environment reaps the benefits of eSentire's Controlled Autonomy approach and the refined protections delivered across our entire customer base.

How does eSentire approach AI security compared to other "AIDR" products?

Guardrails catch known patterns; novel attacks need human adjudication. Other vendors sell you a dashboard and leave the monitoring to your team. Atlas AIDR includes our 24/7 SOC and Elite Threat Hunters because AIDR without a SOC is like EDR without MDR. We don't just give you a tool to run—we provide a managed outcome, watching the AI supply chain, identifying supply-chain drift, and investigating anomalous spend as a compromise signal, 24/7.

Run Atlas in Your Environment.

Start today and see how Atlas delivers faster than the attacker.