Connects to any signal across any vendor stack and powers adaptive AI Operatives that expose, detect, and neutralize cyberattacks.
Atlas Operations CenterSee what our SOC sees, review investigations, and see how we are protecting your business.
Technology IntegrationsAtlas connects to any signal across your current security tools. Whatever you're running, we're running with you.
Extend your team with immediate expertise, hands-on remediation, and the human accountability layer that boards, regulators, and cyber insurers require.
Threat Response UnitProactive threat intelligence, original threat research and a world-class team of seasoned industry veterans.
Response and RemediationPairs machine-speed containment with human judgment, delivering full threat response that's policy-bounded, reversible, and explainable.
MDR that moves first, multi-signal attack surface coverage, and 24/7 Elite threat hunters working as one continuous security program across any vendor stack.
Get unlimited Incident Response with threat suppression guarantee- anytime, anywhere.
Atlas Preempt deploys AI Operatives to continuously validate attack paths exposing attacker targets of opportunity before they take advantage.
Protect insurance operations from cyber attacks.
ConstructionSecure project data and jobsite operations.
FinanceDefend financial services from cyber disruption.
LegalSafeguard client data and legal operations.
ManufacturingStop threats before they disrupt production.
Private EquityProtect portfolio companies from cyber risk.
HealthcareDefend patient data and clinical operations.
RetailProtect customer data and retail operations.
Food SupplySecure the food supply chain from cyber threats.
Government and EducationProtect public sector and education systems.
Automotive DealershipsSecure dealership operations and customer data.
Stop ransomware before it spreads.
Identity ResponseStop identity-based cyberattacks.
Zero Day AttacksDetect and respond to zero-day exploits.
Cybersecurity ComplianceMeet regulatory compliance mandates.
Third-Party RiskDefend third-party and supply chain risk.
Cloud MisconfigurationEnd misconfigurations and policy violations.
Cyber RiskAdopt a risk-based security approach.
Mid-Market SecurityMid-market security essentials to prioritize.
Sensitive Data SecurityProtect your most sensitive data.
Cyber InsuranceMeet insurability requirements with MDR.
Cyber Threat IntelligenceOperationalize cyber threat intelligence.
Security LeadershipBuild a proven security program.
eSentire's Threat Response Unit (TRU) has identified an increase in vishing attacks leading to data extortion against organizations in the legal, healthcare, and financial service…
On October 20th, the PHP Group announced an upcoming emergency security release to address two critical vulnerabilities impacting PHP, each rated CVSS 9.2. PHP has stated that technical…
eSentire is a leader in Controlled Autonomy SecOps, protecting thousands of organizations across 35+ industries around the world. Founded in 2001, the company’s Controlled Autonomy SecOps operating model pairs agentic AI operatives with engineered human-judgment controls, delivering expert-depth security outcomes at machine speed without ceding accountability to opaque automation.
About Us Leadership Careers Event Calendar → Newsroom → Aston Villa Football Club →
We provide sophisticated cybersecurity solutions for Managed Security Service Providers (MSSPs), Managed Service Providers (MSPs), and Value-Added Resellers (VARs). Find out why you should partner with eSentire, the Authority in Managed Detection and Response, today.
Search our site
Multi-Signal MDR with 300+ technology integrations to support your existing investments.
24/7 SOC-as-a-Service with unlimited threat hunting and incident handling.
We offer three flexible MDR pricing packages that can be customized to your unique needs.
The latest security advisories, blogs, reports, industry publications and webinars published by TRU.
Compare eSentire to other Managed Detection and Response vendors to see how we stack up against the competition.
See why thousands of organizations globally have chosen eSentire for our MDR Solution.
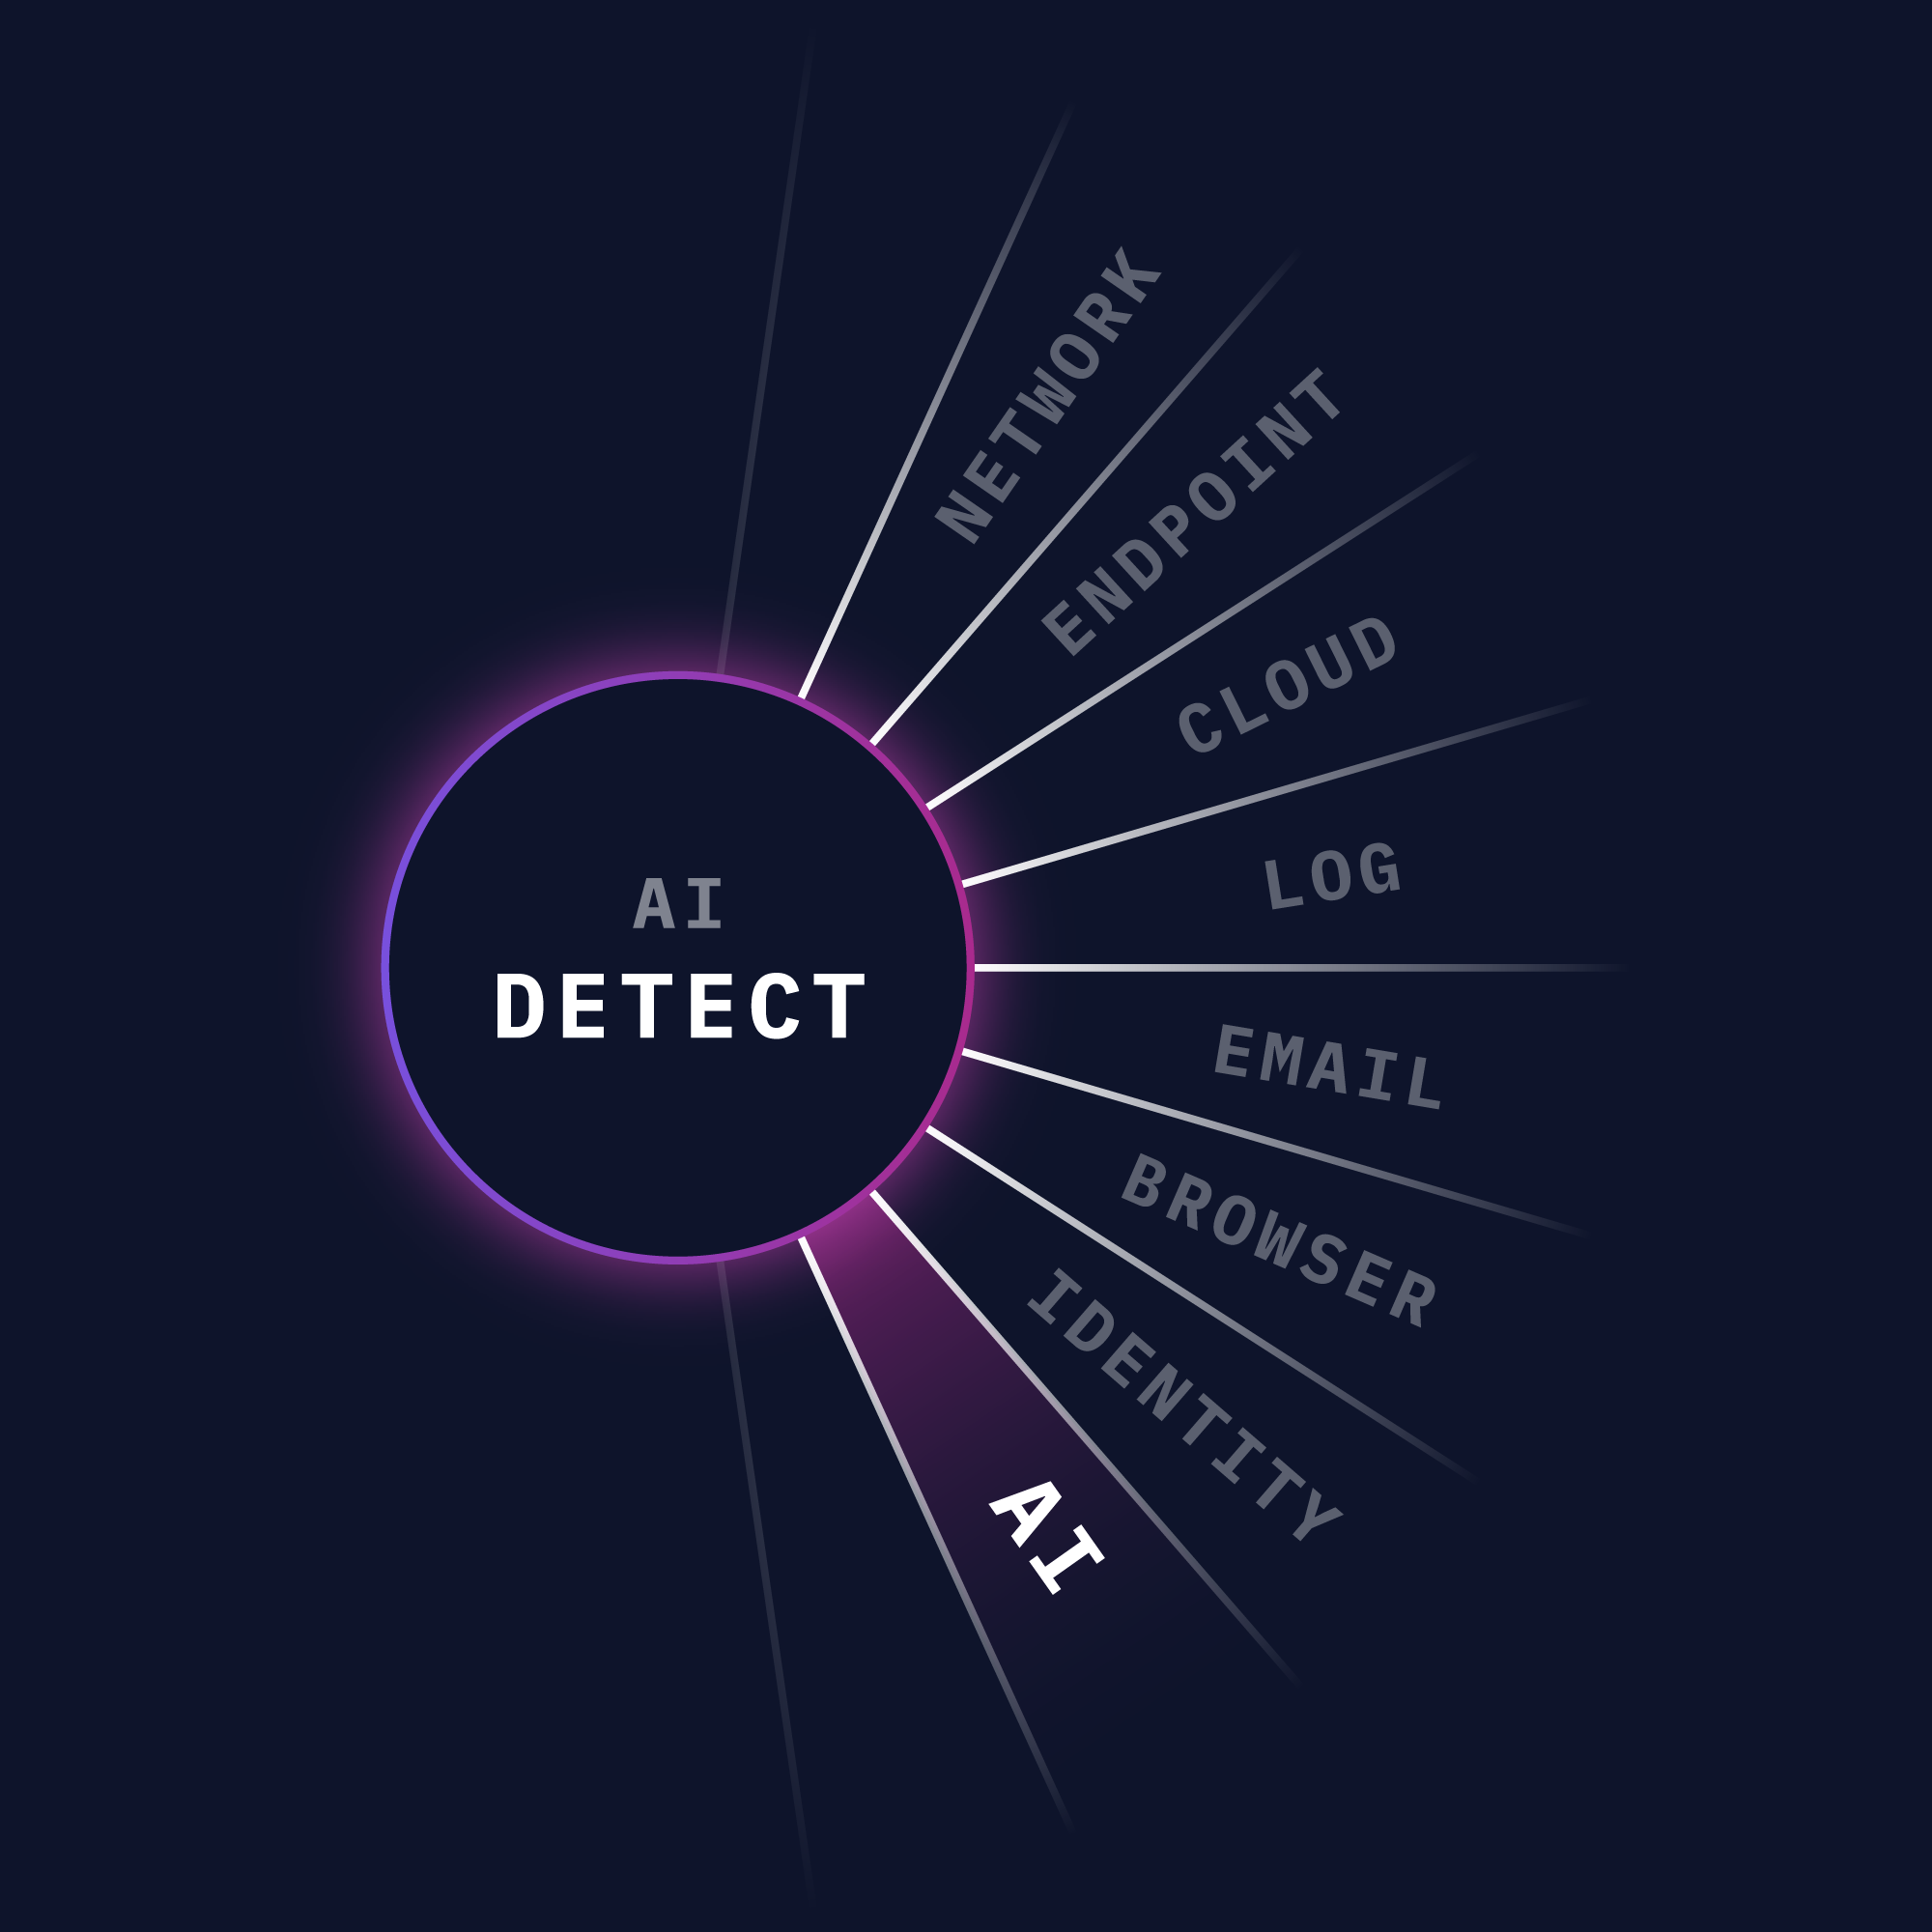
Atlas AIDR brings AI activity on your desktops, in the browser, and across Microsoft 365 Copilot into one record, with detection, blocking rules, and the eSentire SOC behind it.
Build a QuoteAtlas AIDR Capabilities
See Atlas AIDR in Action
Atlas AIDR vs Typical AI Security Tooling
FAQ
Resources
Agents, models, MCP servers, and browser AI tools, plus who's using them.
The MCP servers, plugins, and hooks your agents load, and what depends on them.
Catch secrets, PII, and prompt injection. Block inline in Claude Code and Claude Cowork, and block, warn, redact or just record in the browser.
Spend is a detection signal. A hijacked agent loop shows up in token burn first.
Shadow AI found across the browser and the network, with prompts tied to a person on the five biggest AI apps.
Prompt text is sealed by default. No one sees it: not your admins, not eSentire, not even the AI that summarizes sessions.
Atlas AIDR closes the gap left by AI tools your existing security stack was never built to see. It plugs directly into the Atlas Platform for AI governance, detection and response, without blocking adoption.
We're continuing to build out Atlas AIDR. Coming soon:
Requests with nothing to block go straight through.
Allow only your company's own ChatGPT, Claude, and other AI accounts.
More accurate token and cost numbers.
The Atlas Outpost LLM Gateway, or your own third-party gateway.
New detections, including the OWASP Top 10 for LLM applications.
Findings, sessions, spend, and supply-chain inventory across desktop and browser AI, in one view. First captured session in minutes.
Atlas AIDR (AI Detection and Response) is a capability in the Atlas Platform. It shows what your AI agents, MCP servers, and browser AI tools are doing, detects secrets, PII, and prompt injection in prompts, and blocks them by rule, with the eSentire SOC behind it.
In five steps.
Unreviewed MCP servers, prompt injection, secrets and PII in prompts, shadow AI in the browser, and anomalous token spend that can signal compromise.
Most AI security tools stop at inventory and detection. Atlas AIDR adds per-request spend as a compromise signal, one record across desktop and browser AI, one console with the rest of your estate, and the eSentire SOC behind it.
Your first captured session arrives in minutes. One install command sets up every AI tool on a computer and keeps itself up to date.
Yes. The Atlas browser extension for Chrome and Edge captures prompts on ChatGPT, Claude, Gemini, Microsoft Copilot, and Perplexity, and each rule can block, warn, redact or just record. You can switch off Gemini in Chrome and Copilot in Edge.
Yes. See Copilot use across Microsoft 365, app by app, in the same record as the rest of your AI. Copilot content stays in Microsoft. AIDR stores none of it. Microsoft Copilot in the browser is a separate product, covered by the extension.
No. Private by design. Prompt text is sealed by default. No one sees it: not your admins, not eSentire, not even the AI that summarizes sessions. When an investigation needs it, a break-glass reveal asks for a reason and logs every read, and you decide who on your team may ask.
Assume your AI is already doing things you cannot account for.